Last issue was supposed to be an announcement of our recent participation in events, conferences and magazines, whether speaking, conducting a workshop or writing about something nasty we had to deal with.
But of all the nasty things we deal with, there’s a very persistent one that, we could say, doesn’t have the best timing. So, after dealing with them, we can finally share some happier news.
DEF CON 34
This year we had a blast at Hacker Summer Camp, aside from having to run from one stage to another a couple of times.
Nelson and I worked all year long to build Haetae, an agent designed to automatically take down malware C2 servers belonging to our weird-hairstyled friends by exploiting vulnerabilities in their own malware components. And it seems quite a few villages liked our idea!
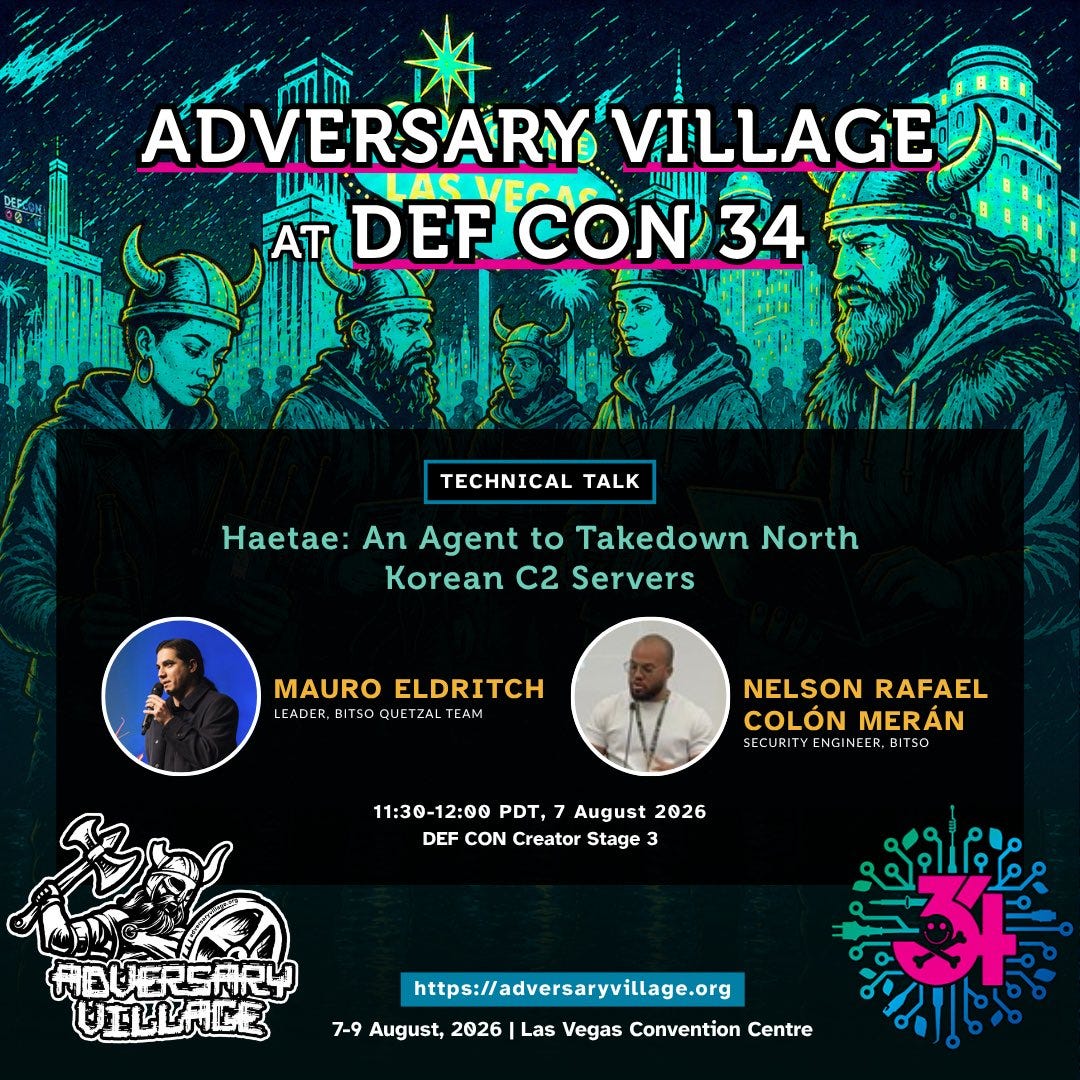
Our first stop was the Adversary Village, where we explained how to build the AI agent itself in the most agnostic way possible, making it suitable for all audiences and adaptable to other malware strains or threat actors.
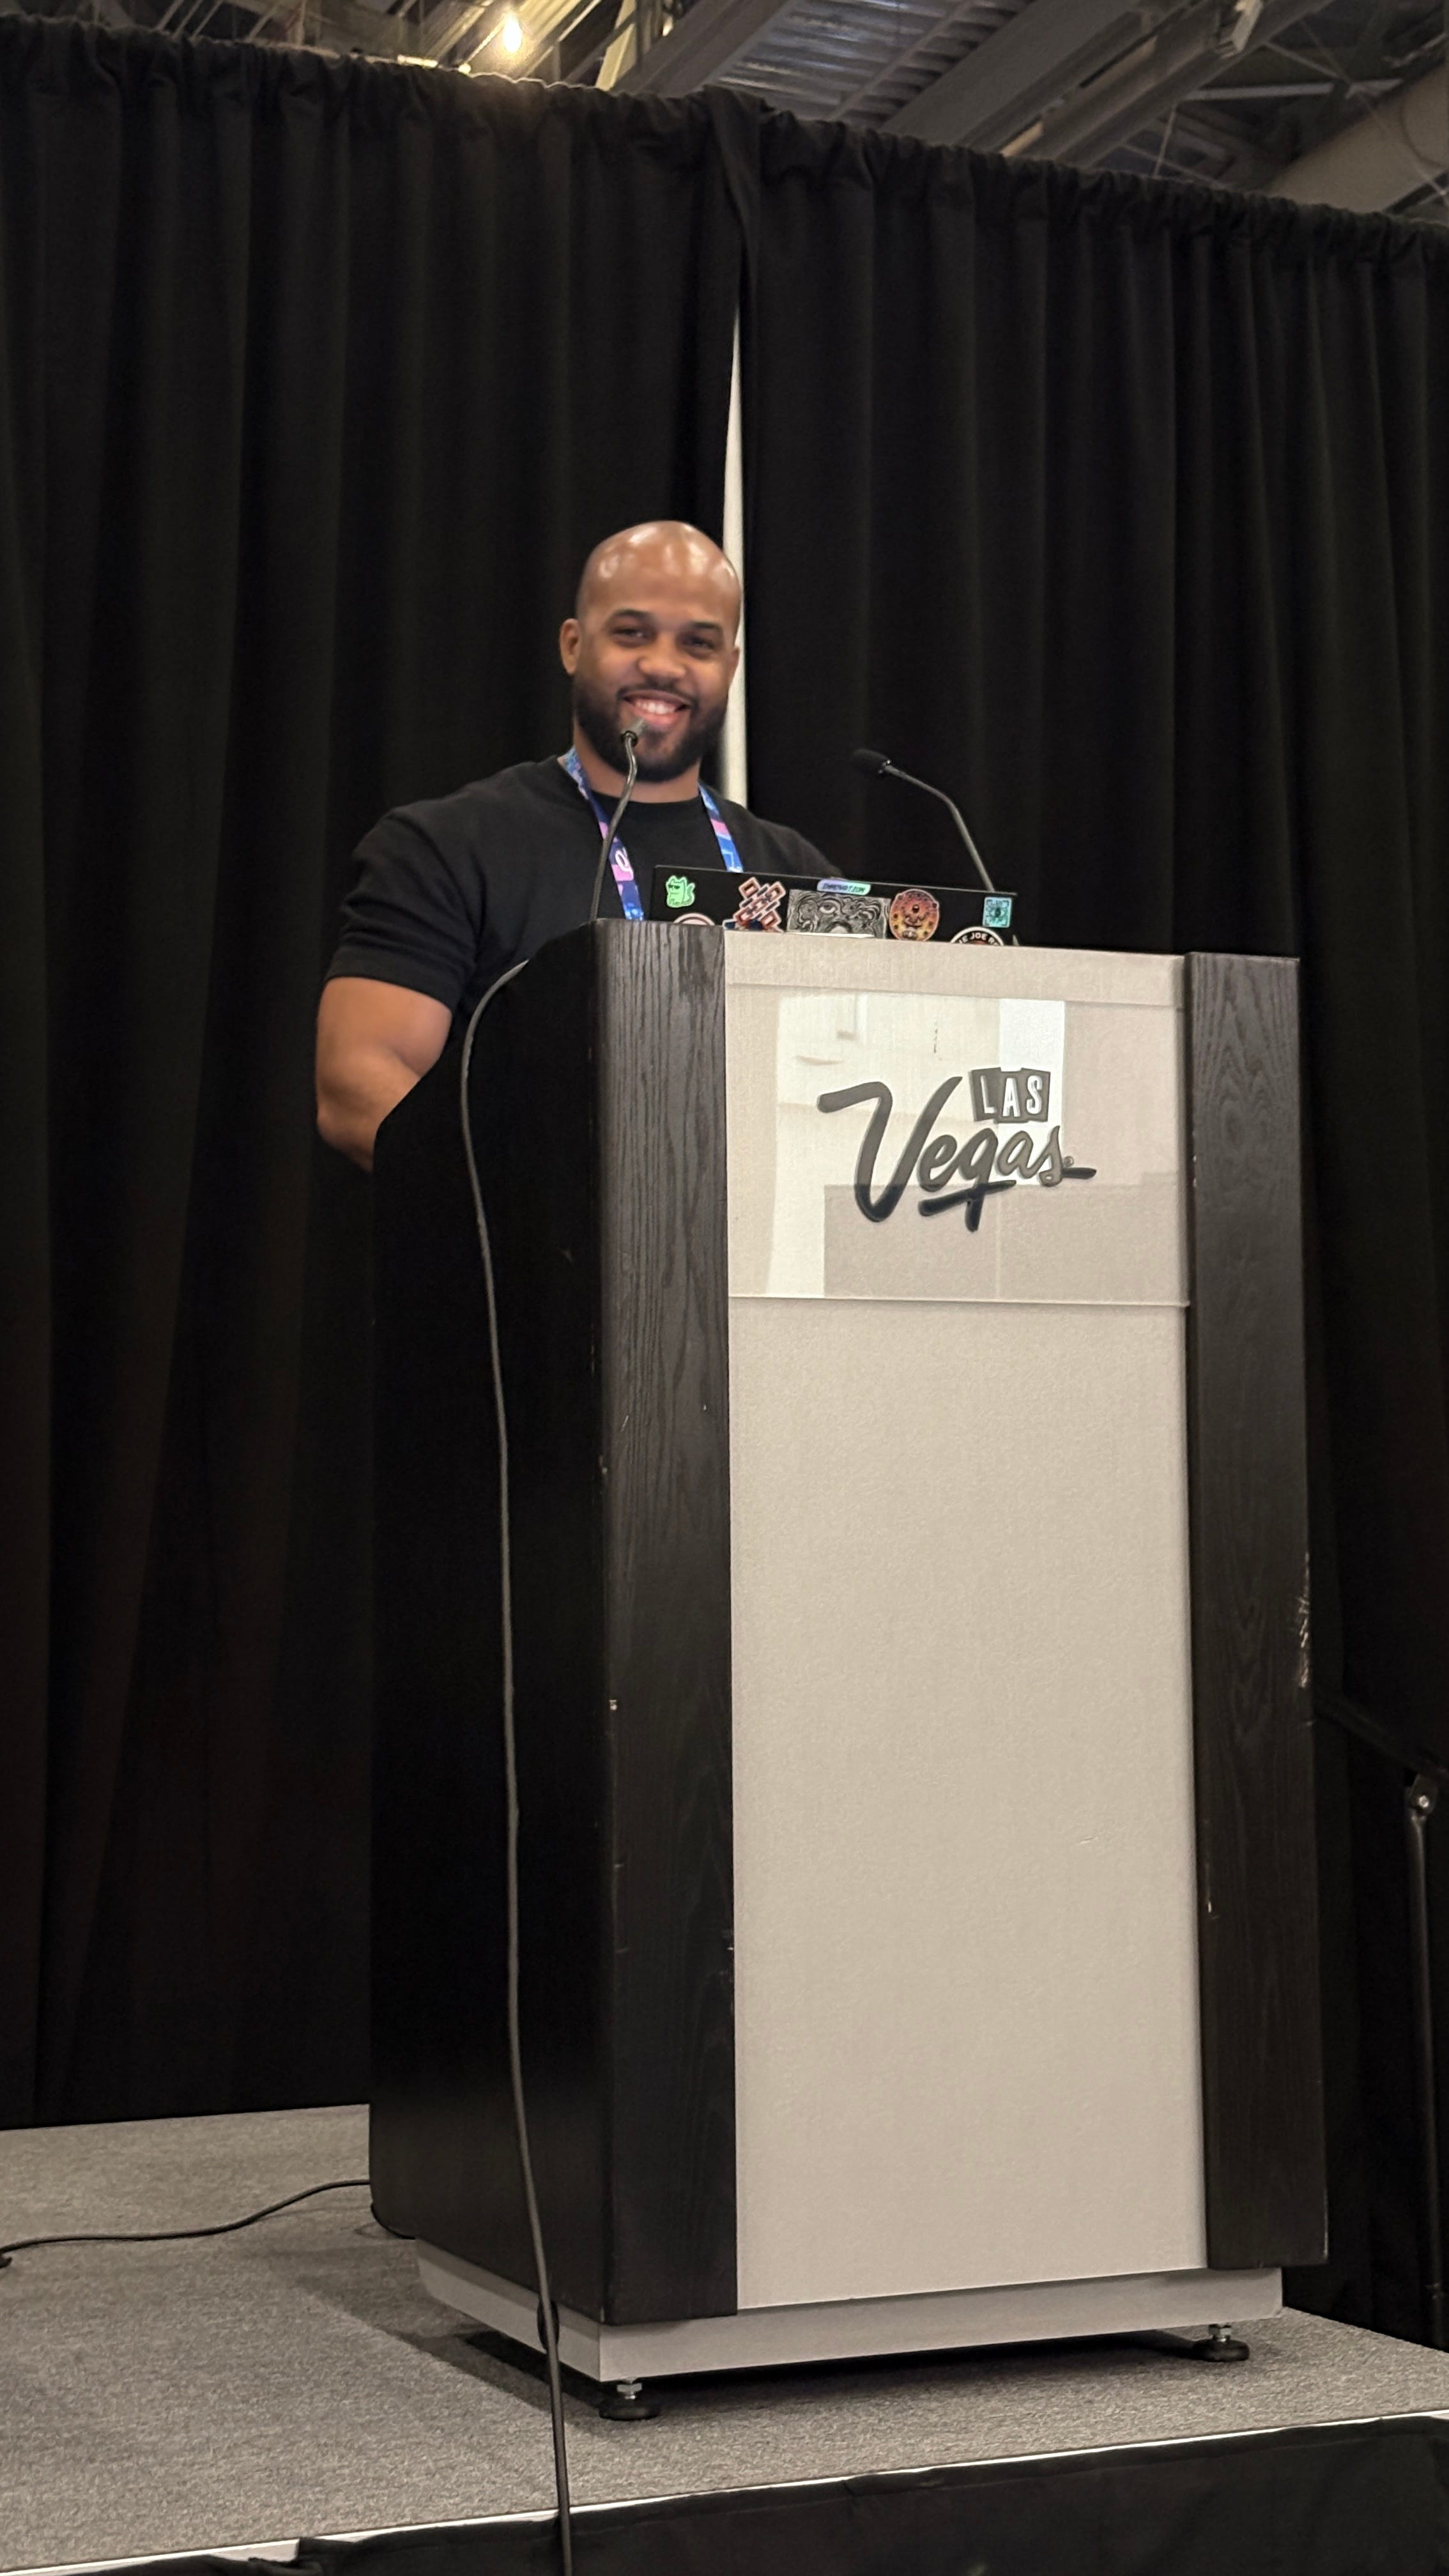
We then moved to the Malware Village, where Nelson dissected the malware strains and explained their vulnerabilities in detail, to everyone’s amusement.
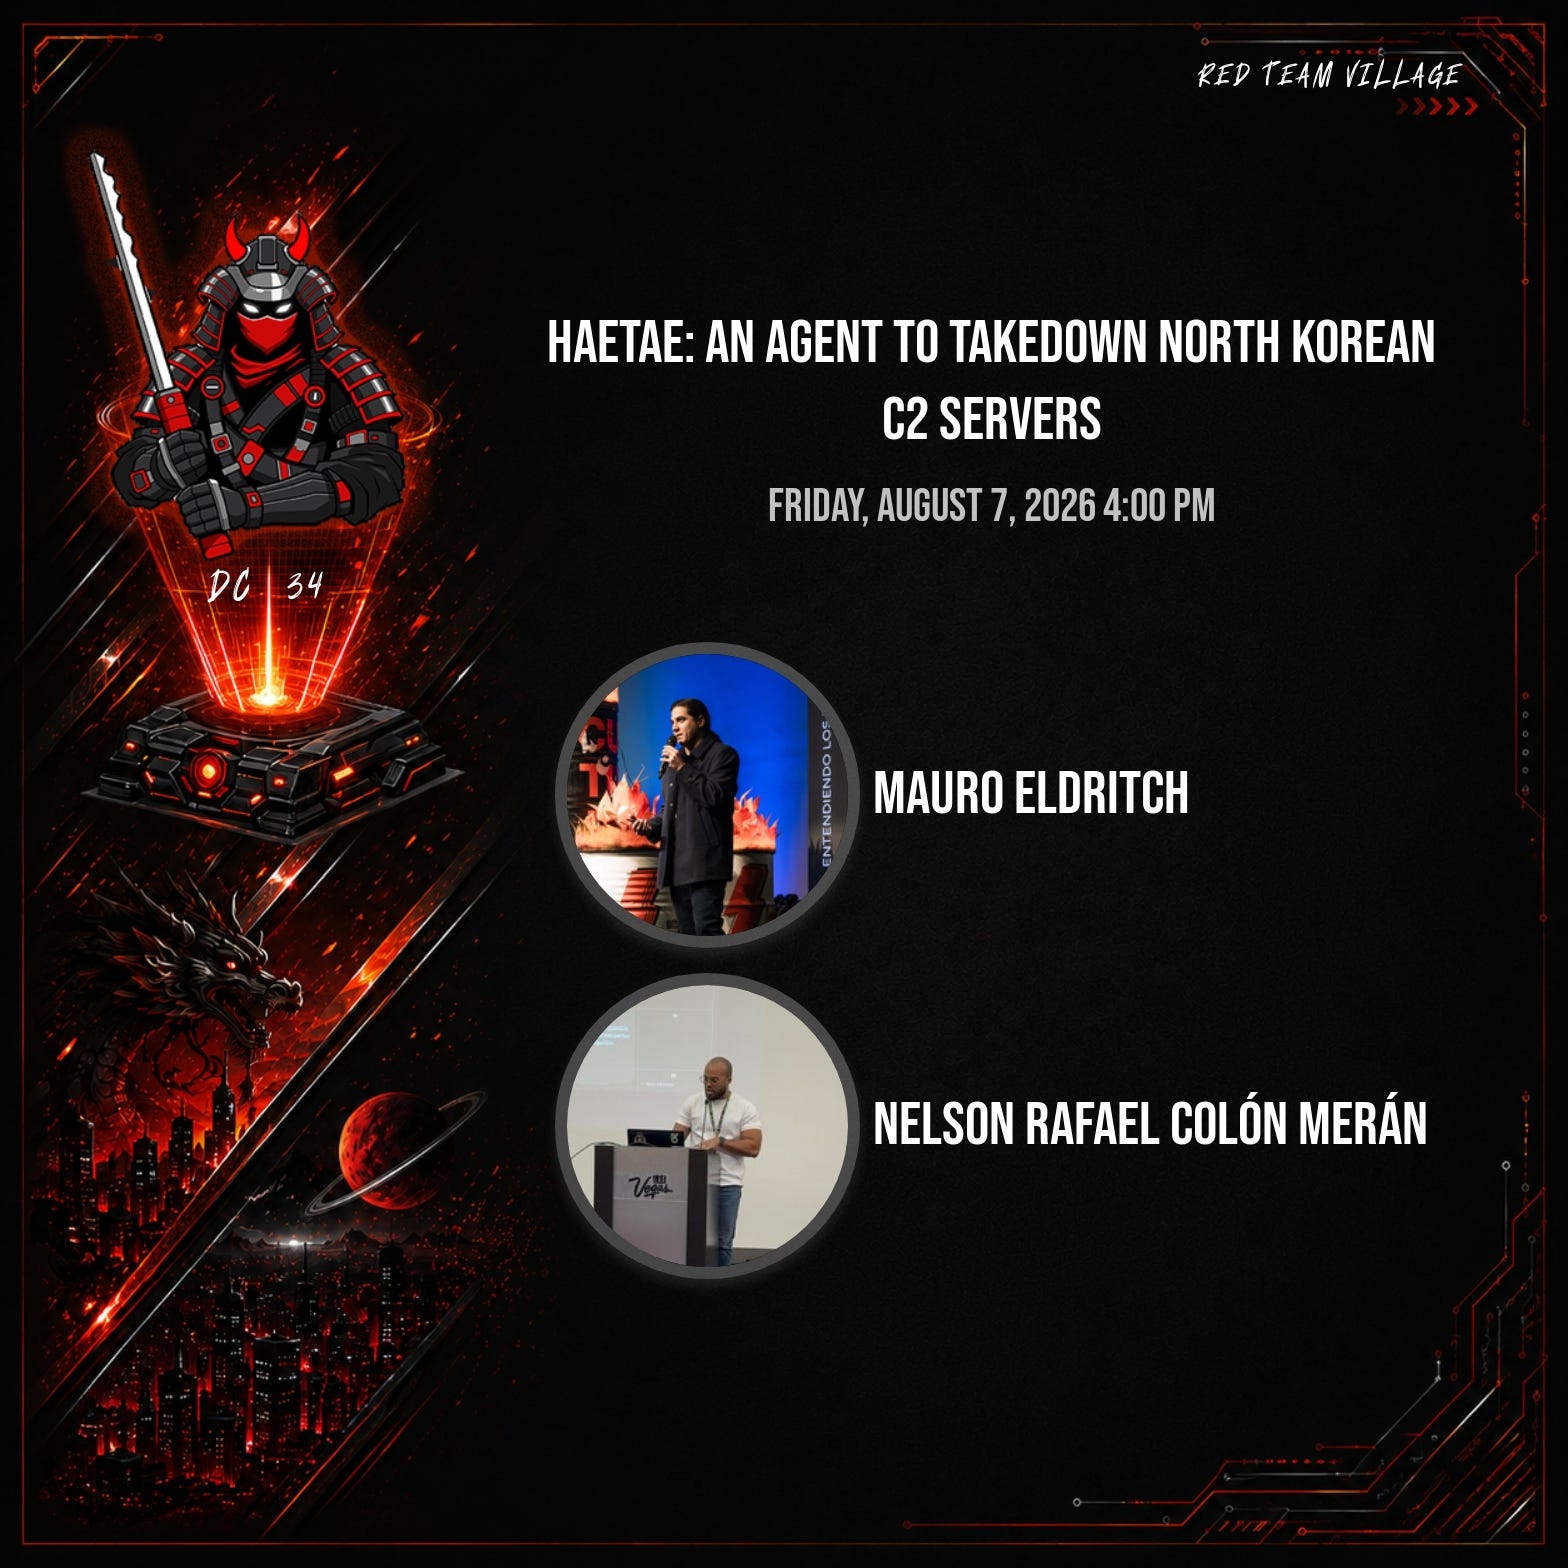
Later on, we moved to the Red Team Village, where we conducted a hands-on workshop that let everyone experience taking down their first malware server.
Then we returned to the Malware Village once more with our talk, “North Korea’s Zoo”, revisiting the latest malware samples that had been thrown at us throughout the year.
DragonJAR and Nerdearla
Next stop was LATAM, specifically Colombia, where we attended DragonJAR, LATAM’s biggest Spanish-speaking hacking conference. There, we spoke about our experience interviewing DPRK IT workers, showing live interviews and analysing the footage.
And just a few days ago, we attended Nerdearla Argentina, one of the best events in South America, with top speakers from all around the world. We presented the same talk, with a surprise at the end.
PagedOut! #9
Of course, we keep supporting the eZine scene, and there’s no better place to do so than PagedOut!, a magazine that brings together one-page articles from writers all around the world: hackers, makers, reversers, crackers, programmers, you name it. And then there’s us, writing about North Koreans.
Sofía wrote a great article from her perspective as a Talent Acquisition Specialist on interviewing fake IT workers, explaining what the recruitment process looks like from the inside and the signals that may emerge along the way.
For my part, I wrote about the recent wave of ClickFix attacks and how they work, the different excuses attackers use, the social engineering from the attackers’ perspective, and how you ultimately end up infecting yourself.
You can read the full issue here, or you can download it as a PDF here.
Outro
So this is where we stand now: creating content to help spread awareness, fend off threat actors, and make this space a little bit safer, one interview or takedown at a time.
As usual,
stay safe,
don’t hire North Koreans,
and don’t get rekt.